
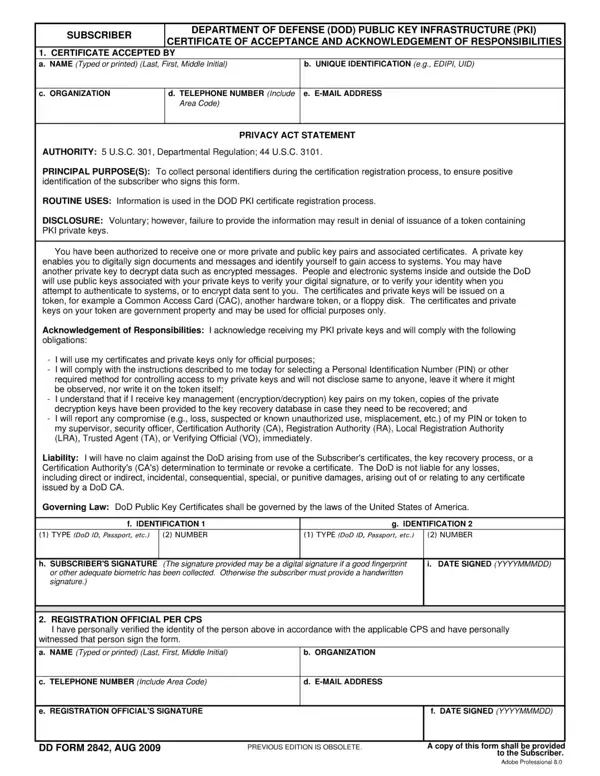

DD Form 2842 at a glance
What it is: DD Form 2842 (APR 2026) is the Subscriber Department of Defense (DoD) Public Key Infrastructure (PKI) Certificate of Acceptance and Acknowledgement of Responsibilities.
Who signs: Part 2, Block i: The subscriber must sign in this block. The signature should match the name provided in Block a. The Registration Official will indicate in this block if the Subscriber is incapable of signing. (Note: For the electronic version of this form, the Subscriber's signature will be automatically applied.) Part 3, Block e: Date will automatically populate to current date (YYYYMMMDD). Block f: The Authorized Official must sign in this block. (Note: For the electronic version of this form, the Registration Official's digital signature will be automatically applied.)
A filled-in DD Form 2842 example: a subscriber accepts a server certificate
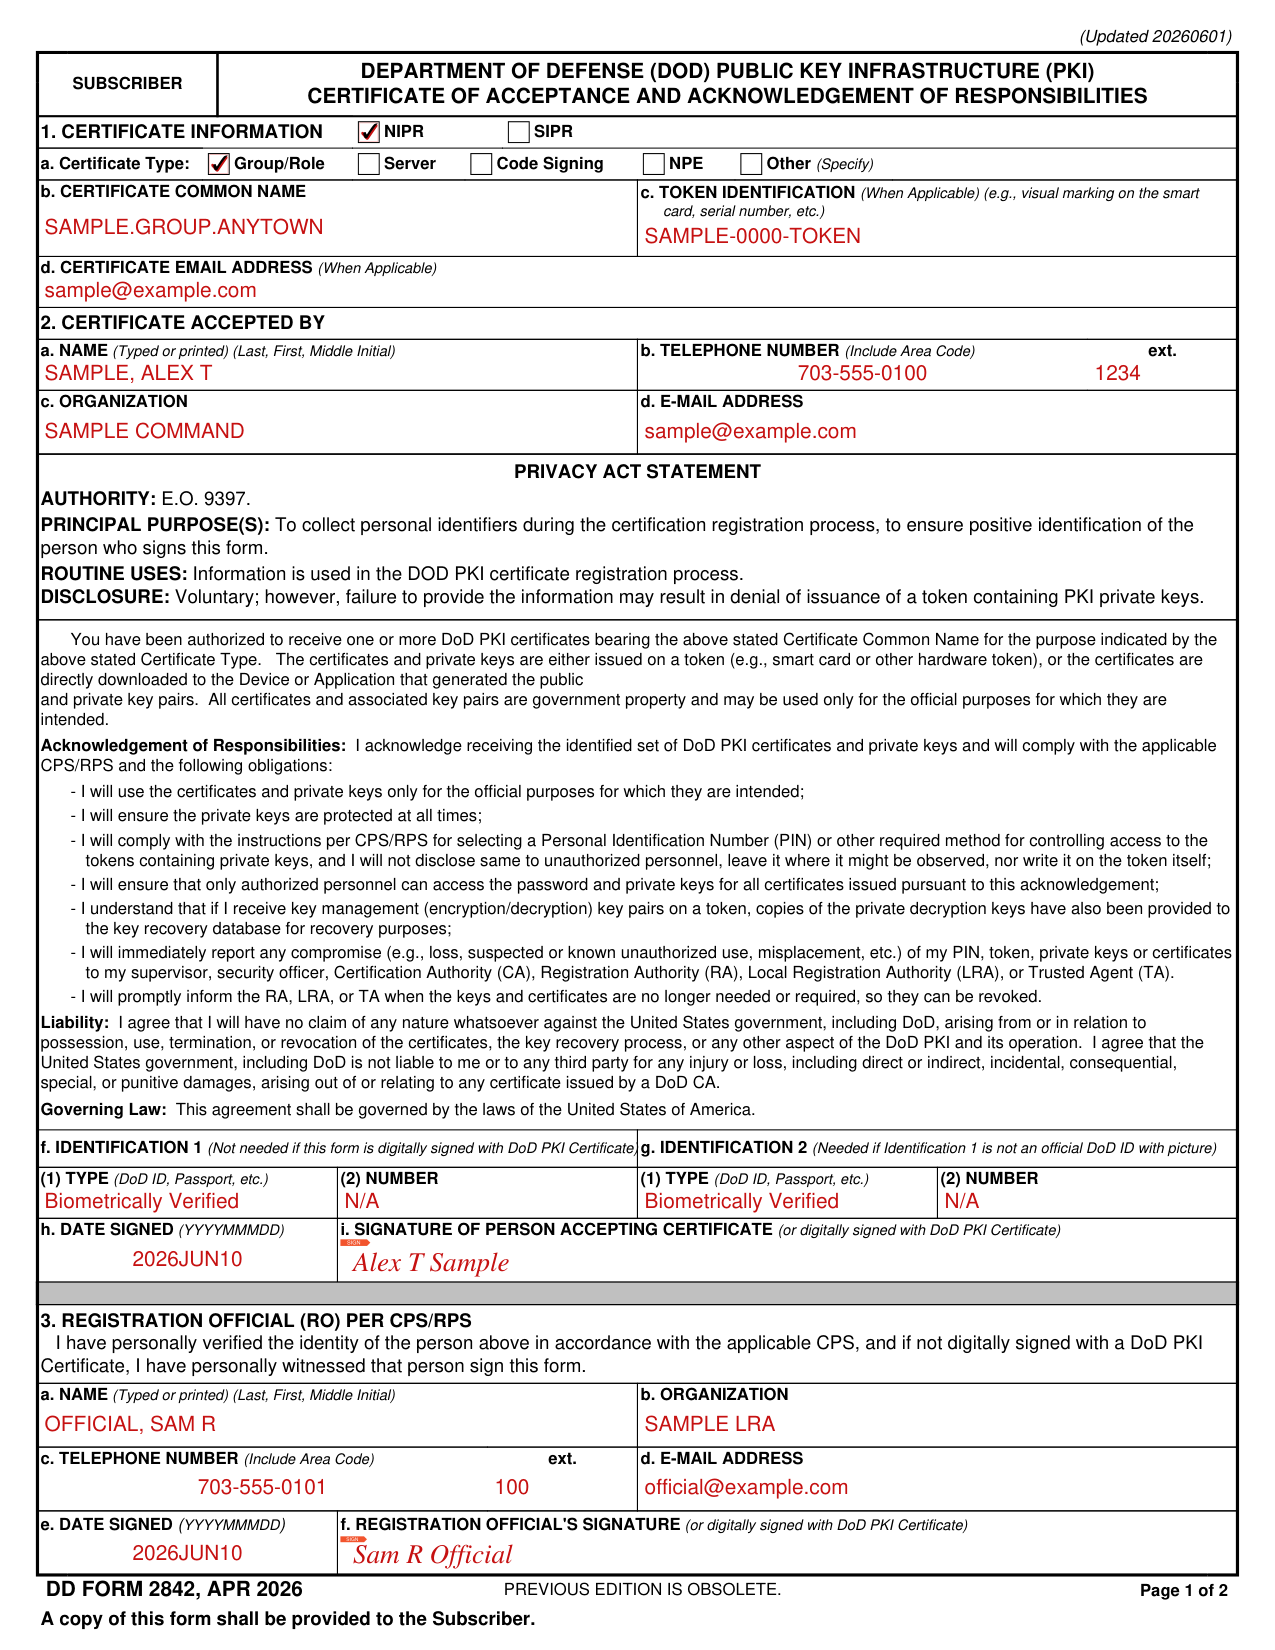
How to fill out DD Form 2842, box by box
Certificate Information
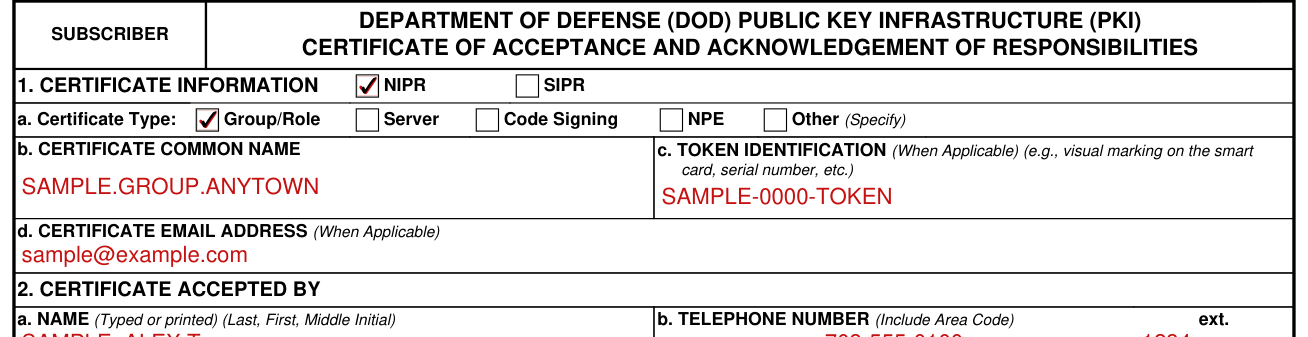
The Subscriber completes the certificate information and a Registration Official verifies it; if the electronic version of this form is used, some blocks may automatically be filled and only the remaining blocks require completion. Select the NIPR or SIPR check box.
In Block a, select the appropriate certificate check box.
In Block b, enter the Certificate Common Name. In Block c, enter the Token Identification (When Applicable). In Block d, enter the Certificate Email Address. Part 2 is the Certificate Acceptance by Subscriber.
Certificate Accepted By
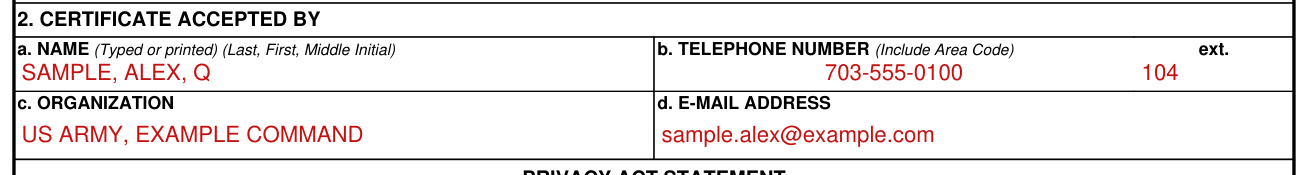
In Block a of Certificate Acceptance by Subscriber, enter your full name as Last Name, First Name, MI.
In Block b, enter a 7 digit DSN telephone number or a 10 digit commercial telephone number (i.e. area code + 7 digit number) and extension if necessary.
In Block c, enter the Organization (branch of service, major command, or duty station).
In Block d, enter the Subscriber's email address. Read the Privacy Act Statement, Acknowledgment of Responsibilities, Liability, and Governing Law statements.
Identification 1 and Identification 2

In Block f (1), enter a descriptive name for a federal government-issued identification credential with a picture, for example Military ID card or Passport. Enter a unique identification number from that credential in Block f (2).
Identification 1 is not needed if this form is digitally signed with DoD PKI Certificate.
Identification 2 is needed if Identification 1 is not an official DoD ID with picture.
If a federal government issued identification credential with a picture is available, then blocks g(1) and g(2) are not required to be completed.
However, if a federal government identification credential with a picture is not available and the Registration Official cannot be biometrically verified, two non-federal government-issued identification cards are required. At least one of the identification cards must show the Subscriber's picture (for example, a driver's license). Enter a descriptive name for the first credential in Block g (1) and a unique identification number from that credential in Block g (2).
If the Registration Official can be biometrically verified, no identity documents are required; enter "Biometrically Verified" in Blocks f(l) and g(l) and "N/A" in f(2) and g(2).
Date signed and signature of person accepting certificate

Enter the date signed (YYYYMMMDD) and the signature of the person accepting certificate (or digitally signed with DoD PKI Certificate).
In Block h, the current date will automatically be filled in (YYYYMMMDD).
Registration Official
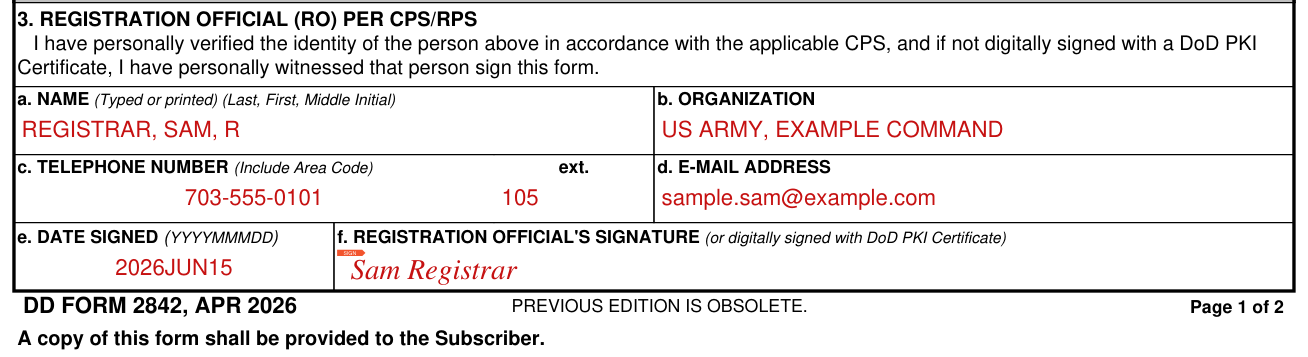
In box 3, the Registration Official has personally verified the identity of the person in accordance with the applicable CPS, and if not digitally signed with a DoD PKI Certificate, has personally witnessed that person sign this form.
Part 3, Identity Verification by Registration Official, will be completed by an Authorized Official per the CPS at the time of the Registration Official's registration; if the electronic version of this form is used, some blocks may be automatically filled and only the remaining blocks require completion. In Block a, enter full name as Last Name, First Name, and MI. In Block b, enter branch of service, major command, and duty station.
In Block c, enter 7 digit DSN telephone number or 10 digit commercial telephone number (i.e. area code + 7 digit number). In Block d, enter current e-mail address.
More rules for DD Form 2842
You acknowledge receiving the identified set of DoD PKI certificates and private keys and will comply with the applicable CPS/RPS and the following obligations:
Use the certificates and private keys only for the official purposes for which they are intended. Ensure the private keys are protected at all times. Do not disclose the PIN to unauthorized personnel, leave it where it might be observed, nor write it on the token itself. Ensure that only authorized personnel can access the password and private keys for all certificates issued pursuant to the acknowledgement. If you receive key management (encryption/decryption) key pairs on a token, copies of the private decryption keys have also been provided to the key recovery database for recovery purposes. Immediately report any compromise (e.g., loss, suspected or known unauthorized use, misplacement, etc.) of the PIN, token, private keys or certificates to the supervisor, security officer, Certification Authority (CA), Registration Authority (RA), Local Registration Authority (LRA), or Trusted Agent (TA). Promptly inform the RA, LRA, or TA when the keys and certificates are no longer needed or required, so they can be revoked.
You agree to have no claim of any nature whatsoever against the United States government, including DoD, arising from or in relation to possession, use, termination, or revocation of the certificates, the key recovery process, or any other aspect of the DOD PKI and its operation.
This agreement shall be governed by the laws of the United States of America.
Sources
[1] DD Form 2842 (APR 2026), Subscriber Department of Defense (DoD) Public Key Infrastructure (PKI) Certificate of Acceptance and Acknowledgement of Responsibilities, Washington Headquarters Services (the Official source link on this page).